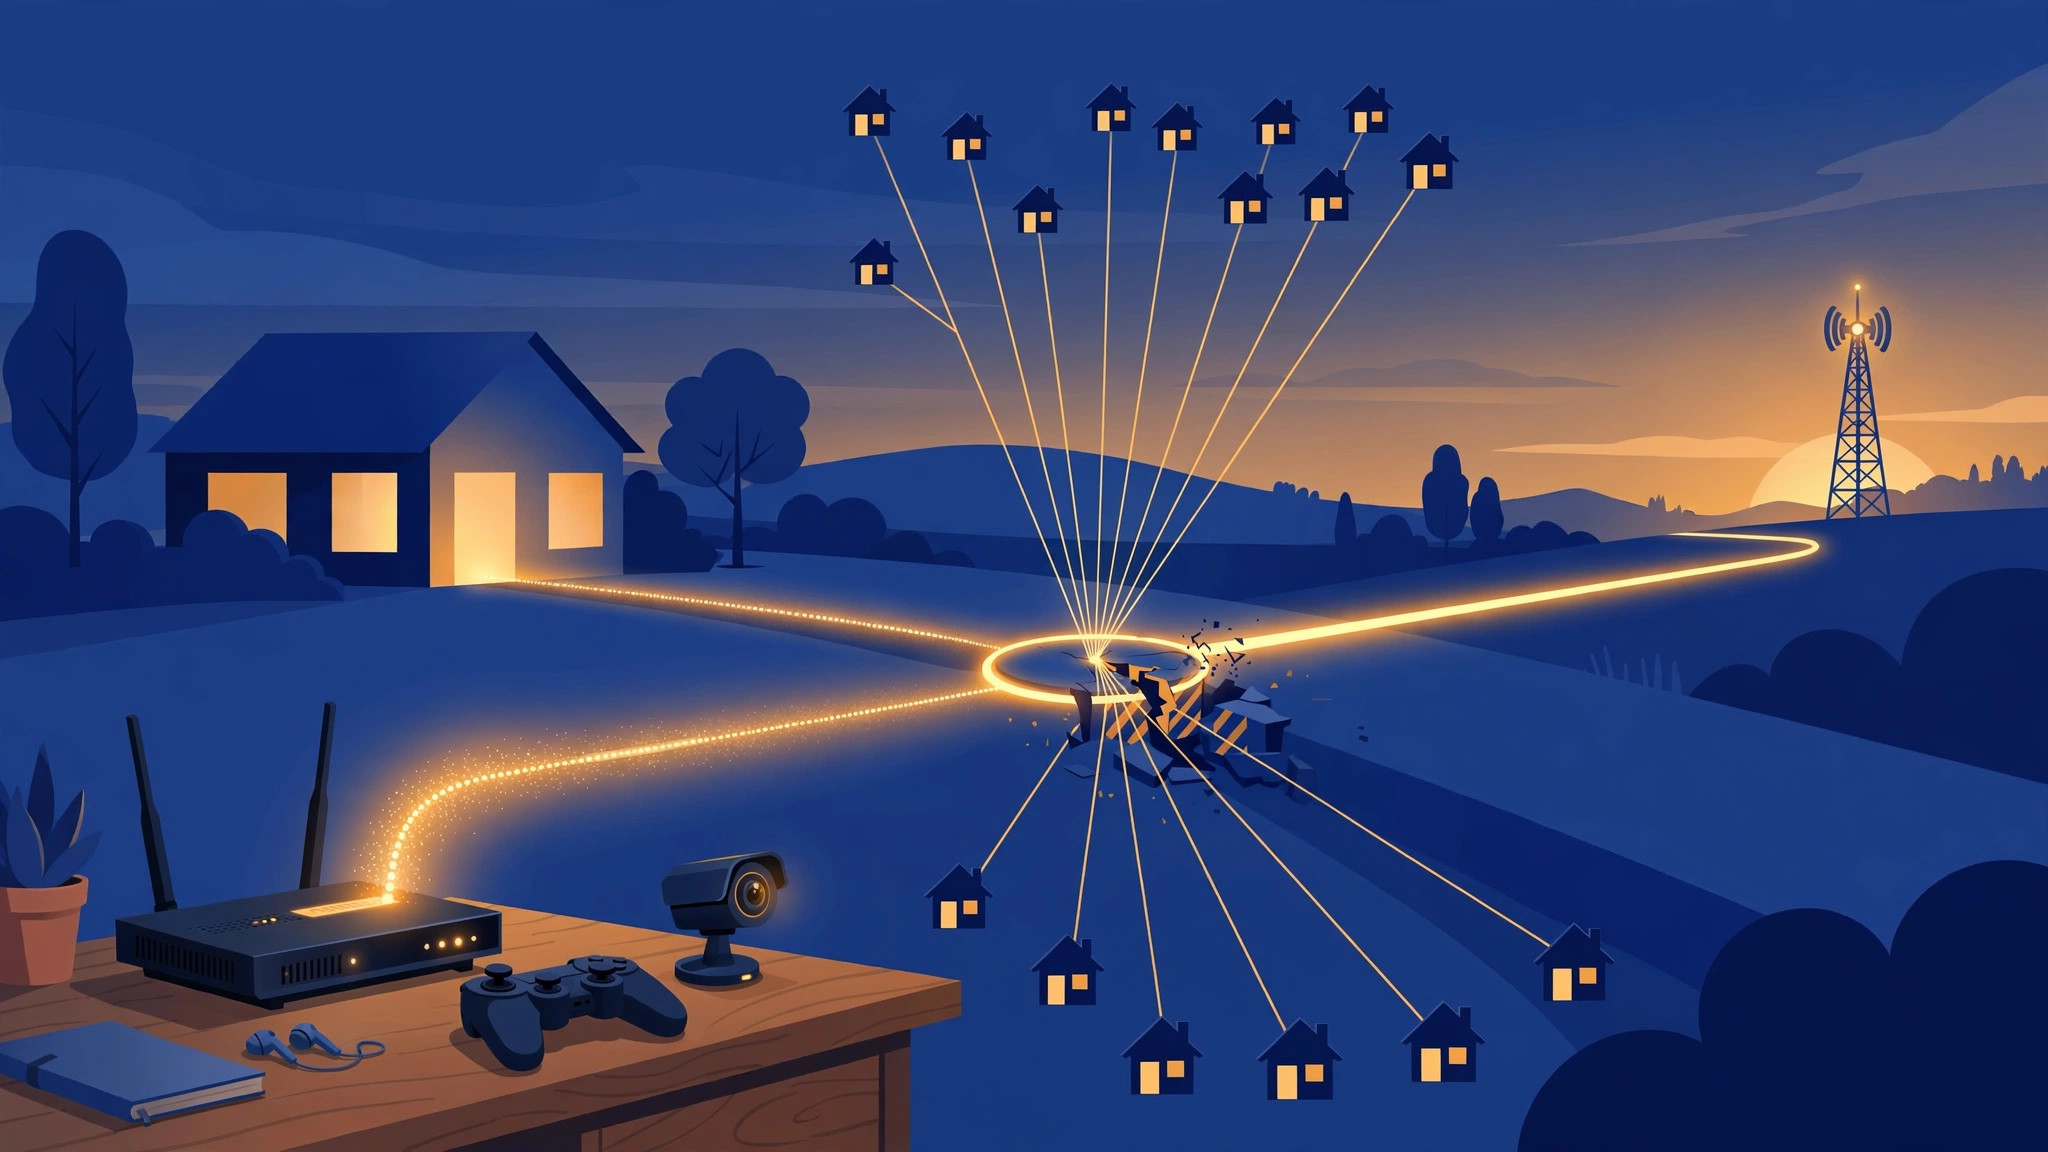
You bought 5G home internet for its speed, set up a game server or tried to check your security cameras from work — and nothing connects. The problem is not your router. It is CGNAT, and no router setting can fix it. Here is what CGNAT breaks, how to check if you are behind it, and what actually works.
In brief
- 5G home internet blocks port forwarding with CGNAT. Which Australian providers use it, and the workarounds that get game servers and remote access working.
- What CGNAT is, in one paragraph: Every device on the internet needs an IP address.
- What CGNAT breaks: If any of these matter to you, CGNAT is a deal-breaker, not an inconvenience:
- The 5G providers: who uses CGNAT
- How to check if you are behind CGNAT: Before changing anything, confirm CGNAT is actually your problem — a misconfigured router looks identical from the outside:
5G home internet is now a genuine alternative to the NBN in Australia: Telstra, Optus, TPG, Vodafone, SpinTel and others sell plug-in modems with download speeds from 50 Mbps to over 200 Mbps, often cheaper than an equivalent NBN plan. But there is a catch that appears in none of the comparison tables. Most 5G home internet services run behind Carrier-Grade NAT (CGNAT) — a second layer of address-sharing inside the provider’s network that makes inbound connections to your home impossible. Port forwarding, hosting a game server, remote access to your cameras or NAS, and some smart-home setups simply do not work. Vodafone discloses CGNAT on its own 5G plan page; TPG and SpinTel disclose it in their support pages. Telstra says it does not use CGNAT at all. Optus publishes no CGNAT statement we could find.
What CGNAT is, in one paragraph
Every device on the internet needs an IP address. IPv4 addresses ran out years ago, so your home router already shares one public address among all your devices — that is ordinary NAT, and it works fine because your router knows which device asked for what. CGNAT adds a second layer: your provider puts hundreds of customers behind a single public address. Your router gets a private address from the provider, and the provider translates it outbound. Outbound connections (browsing, streaming, video calls) work because your devices initiate them. Inbound connections fail because there is no public address that leads to your router — the public address belongs to the provider, shared with hundreds of strangers, and there is no rule forwarding anything to you.
What CGNAT breaks
If any of these matter to you, CGNAT is a deal-breaker, not an inconvenience:
- Port forwarding. The classic case. You forward a port on your router — say 25565 for a Minecraft server — and friends still cannot connect. The rule is correct; it just never receives traffic, because the traffic stops at the provider’s NAT layer, one step before your router.
- Hosting game servers. Minecraft, Valheim, Terraria, Ark, or any game where friends connect to your machine. Your friends need an address that reaches your house. Behind CGNAT, there is not one.
- Remote access to cameras, NAS, and home automation. Viewing security camera footage remotely, reaching your NAS files from work, or accessing a Home Assistant dashboard from outside the house all depend on inbound connections. TPG’s support pages list exactly these as things that “will not work” on its Home Wireless Broadband: port forwarding, web hosting, smart-home access and similar services.
- Remote desktop and SSH into a home machine. Connecting to your home PC from elsewhere, or SSHing into a Raspberry Pi, fails for the same reason.
- Some peer-to-peer and VPN setups. Certain VPN configurations and peer-to-peer applications that rely on direct inbound connections can degrade or fail, though most consumer VPNs (which make outbound connections) work fine.
What CGNAT does not break: browsing, streaming, video calls, online gaming as a player (you connect to the game’s servers — outbound), downloads, and cloud services. If you only consume the internet, you will never notice CGNAT. The problem is specific to people who want the internet to reach into their home.
The 5G providers: who uses CGNAT
This is the table nobody publishes. The honest version is that only one provider states its position plainly on its own plan page:
| Provider | 5G home internet behind CGNAT? | Opt-out / public IP? | Status of this information |
|---|---|---|---|
| TPG | Yes — TPG’s support FAQ says its Home Wireless Broadband uses CG-NAT, and lists port forwarding, web hosting and smart-home access as not working | No opt-out published | Confirmed (support FAQ — the 5G plan page itself carries no CGNAT wording) |
| Optus | No CGNAT statement found on Optus’s own pages | Optus’s static-IP page describes static IPs for business Fixed Broadband customers; no 5G static-IP option found | Unverified — ask Optus in writing before ordering |
| Telstra | No — Telstra’s support page states “Telstra doesn’t use CGNAT” | Static IP $10/month for nbn and opticomm | Confirmed (general statement — no 5G-specific CGNAT wording found) |
| Vodafone | Yes — Vodafone’s own 5G plan page FAQ states 5G Home Broadband uses CG-NAT, with the same non-working list as TPG | No opt-out published | Confirmed (primary source — the clearest disclosure in the market) |
| SpinTel | Yes — CGNAT is default on 5G; port forwarding “is not possible” | No opt-out on 5G (“there is no way to opt out”) | Confirmed (SpinTel knowledge base) |
Two things to take from that table. First: Vodafone deserves credit for the clearest disclosure in the market — its 5G plan page states the service uses CGNAT and lists exactly what will not work, in plain language, before you buy. TPG and SpinTel disclose the same in their support pages. Second: the gaps are Telstra and Optus, in opposite directions. Telstra says it does not use CGNAT, so its 5G service should not have this problem — though we found no 5G-specific statement. Optus publishes no CGNAT statement at all. If you are considering Optus 5G home internet and you need inbound access, do not assume anything from a comparison page. Ask the provider, in writing, before you order: “Does this service use CGNAT, and can I get a public IPv4 address?” Their answer is the only one that counts.
Note also that CGNAT is not unique to 5G. Some NBN providers use CGNAT too — the difference is that on NBN you usually have an escape: many providers offer a free opt-out or a static IP for around $5 a month (see the NBN section below). On 5G home internet, there is generally no escape hatch at all — with the exception of Telstra, which says it does not use CGNAT.
How to check if you are behind CGNAT
Before changing anything, confirm CGNAT is actually your problem — a misconfigured router looks identical from the outside:
- Log into your router and find its WAN (internet) IP address.
- Compare it with your public IP. Search “what is my IP” in a browser. If the two addresses differ, there is another NAT layer upstream — very likely CGNAT.
- Check the range. If your router’s WAN address starts with 100.64.x.x (the 100.64.0.0/10 range reserved for carrier-grade NAT), you are behind CGNAT. A WAN address in the 10.x.x.x, 172.16.x.x, or 192.168.x.x ranges also indicates a private address from your provider.
- Test a port. With a service running and a port-forward rule in place, check the port from outside your network (for example from your phone on mobile data). If it shows closed despite a correct rule and a running service, CGNAT is the likely cause.
A mismatch does not always mean CGNAT — double NAT (two routers in series) looks similar. But if your modem is the only router and its WAN IP is in the 100.64 range, the diagnosis is solid.
Workarounds that actually work
If you are already on a CGNAT connection, these are the real options, in order of practicality:
1. Use a relay or tunnel service (best for most people). Instead of the internet connecting to you, your home device makes an outbound connection to a relay service, and the relay forwards traffic back down that connection. Outbound connections pass CGNAT freely. Options include Cloudflare Tunnel (free for personal use), Tailscale or WireGuard-based tunnels to a cheap VPS, and services like Pinggy that hand your local service a public URL. For a game server, a tunnel to a small VPS is the standard homelab solution; for a dashboard or camera feed, Cloudflare Tunnel is the simplest path. The trade-off: you add a hop (a few tens of milliseconds of latency) and you depend on the relay service.
2. Use a VPN with a port-forwarding or dedicated-IP add-on. Some VPN providers offer port forwarding or a dedicated public IP as a paid add-on. Your home device connects outbound to the VPN, and the VPN’s public IP forwards the chosen ports to you. This works, but you pay a monthly fee, and you are trusting the VPN provider with your traffic. We do not recommend a specific vendor — check current offerings and privacy policies yourself. For how to judge a VPN provider by its audit record, court record and logging policy, see our VPNs Explained guide.
3. Use IPv6, where it is supported. IPv6 gives every device a globally reachable address, bypassing IPv4 NAT entirely — but both ends of the connection must support IPv6, and your provider must offer it on your service. This is a partial fix, not a general one: your friends’ connections and many services still run over IPv4.
4. Switch to a connection with a public IP (the clean fix). If inbound access is a core need rather than a hobby, the honest answer is that 5G home internet is the wrong product. Move to an NBN provider that gives you a public IP or a cheap static-IP option (below), and the whole problem disappears. No workaround beats simply not being behind CGNAT.
What does not work: adding more port-forward rules, enabling UPnP, buying a better router, or changing DNS settings. None of those touch the provider’s NAT layer. If a guide tells you otherwise, it does not understand the problem.
The NBN alternative: providers with a CGNAT escape hatch
If you decide 5G is not for you, the NBN market is much friendlier to inbound access. The pattern, verified on the providers’ own pages: several providers offer a free CGNAT opt-out — Aussie Broadband, Superloop, Dodo and Swoop among them — and static IPs cost $5 a month at Aussie Broadband, Superloop, Dodo, iPrimus and SpinTel (SpinTel also offers a $2-a-month CGNAT opt-out). Optus and Telstra charge $10 a month for a static IP on NBN, and Telstra says it does not use CGNAT at all. Note that iPrimus requires buying the static IP to opt out of CGNAT — there is no free opt-out there. Prices and policies change, so verify the current figure on the provider’s own page before ordering — and when you order, ask for the opt-out or static IP to be applied from day one, not after you discover the problem.
For the full comparison of NBN providers on price, speed, and service, see our Best NBN Providers guide and our 5G vs NBN comparison.
What this means for you
- 5G home internet is a great deal if you only consume the internet — browsing, streaming, gaming as a player. CGNAT will never bother you.
- If you host anything — a game server, cameras, a NAS, remote desktop — 5G home internet from a CGNAT provider is probably the wrong product, and no router setting will fix it. Telstra says it doesn’t use CGNAT, so its 5G service is the exception to check.
- Vodafone warns you on its 5G plan page; TPG and SpinTel disclose CGNAT in their support pages; Telstra says it doesn’t use CGNAT; Optus publishes no statement. For Optus, ask in writing before ordering: “Does this service use CGNAT, and can I get a public IPv4 address?”
- Already stuck behind CGNAT? A relay/tunnel service is the practical fix; a VPN with port forwarding is the paid alternative; switching to an NBN provider with a free CGNAT opt-out is the clean fix.
- Before buying any “CGNAT bypass” product, run the WAN-IP check above and confirm CGNAT is actually your problem.
Sources
- Teleport — remote access behind NAT and CGNAT: why inbound connections and port forwarding fail
- Reviews.org — what CGNAT is, how to check for it, and the opt-out options

Shoaib Hassan
Shoaib Hassan is the founder and editor of AuTechWire, an independent technology publication covering broadband, mobile networks, privacy, startups, and consumer tech.
Related Stories
Apple’s October 28 Event: The First Touch-Screen MacBook Is Finally Coming
In brief Apple confirmed a second October product event — "Pro and tell," held in Los Angeles on…
Cyberpunk 2077 Update 2.5: Everything in the Edgerunners Patch (and What Leaked Early)
In brief CD Projekt Red announced Update 2.5 on October 20, 2026: it goes live October 22 for…
GTA 6 Pre-Orders Hit 6.45 Million — $630 Million Before Launch
One month before launch, Grand Theft Auto VI has already pre-sold an estimated 6.45 million copies — roughly…