Hotel Wi-Fi, airport Wi-Fi, cafe Wi-Fi — the networks you most want a VPN on are the ones most likely to break it. Three causes explain nearly every failure, and they fix in a specific order. Work the ladder below before you blame the VPN.
In brief
- Hotel, cafe and airport Wi-Fi block VPNs in three specific ways: captive portals, blocked ports, deep packet inspection. The fixes, in order, that actually work.
- Why public Wi-Fi breaks VPNs: the three causes
- The fix ladder (in order): Step 1: Disconnect the VPN and complete the captive portal login.
- Special cases
- When to give up on that network: Give up and use mobile data when: the network's terms prohibit VPNs; you have tried the portal login, two protocols, and three servers; or the connection "succeeds" bu…
A VPN that connects instantly at home and dies at the hotel is not broken — it is being blocked, usually by the network’s login page rather than anything malicious. (For what a VPN does and does not protect, see our VPN explainer.) Public Wi-Fi networks intercept, filter, and restrict traffic in ways home networks do not, and VPN traffic is collateral damage. The fixes are mechanical, and the first one resolves the majority of cases in under a minute. This guide applies anywhere in the world; menu names vary slightly between VPN apps, but the underlying steps are the same.
Why public Wi-Fi breaks VPNs: the three causes
Cause 1: The captive portal. Most hotel, airport, and cafe networks make you accept terms or enter a code on a login page before granting real internet access. Here is the trap: if your VPN connects (or tries to) before you complete that login, it encrypts everything — including the unencrypted probe your device uses to detect the login page. The network cannot redirect what it cannot read, so the login page never appears, and you sit there with “no internet” blaming the VPN. A guest-Wi-Fi troubleshooting guide by Purple.ai describes exactly this mechanism: the encrypted tunnel prevents the gateway from issuing the HTTP redirect the captive portal needs. The fix is to log in first, VPN second — always, in that order.
Cause 2: Blocked ports and protocols. Many public networks run firewalls that block the ports VPN protocols use by default. OpenVPN’s own troubleshooting documentation notes that firewalls commonly block the ports used by IPsec and older protocols, and that switching OpenVPN to TCP on port 443 — the port all regular encrypted web traffic uses — often gets around the block, because the network cannot block port 443 without breaking the web itself. Gizmodo’s VPN-blocker guide gives the same advice in plainer terms: an obfuscated protocol or a TCP connection on port 443 usually connects where the defaults fail.
Cause 3: Blocked server IPs. Some networks go further and block the IP addresses of known VPN servers. In that case the protocol is fine but the destination is blacklisted. The fix is a different server, not a different protocol — try two or three servers in the same country before changing anything else.
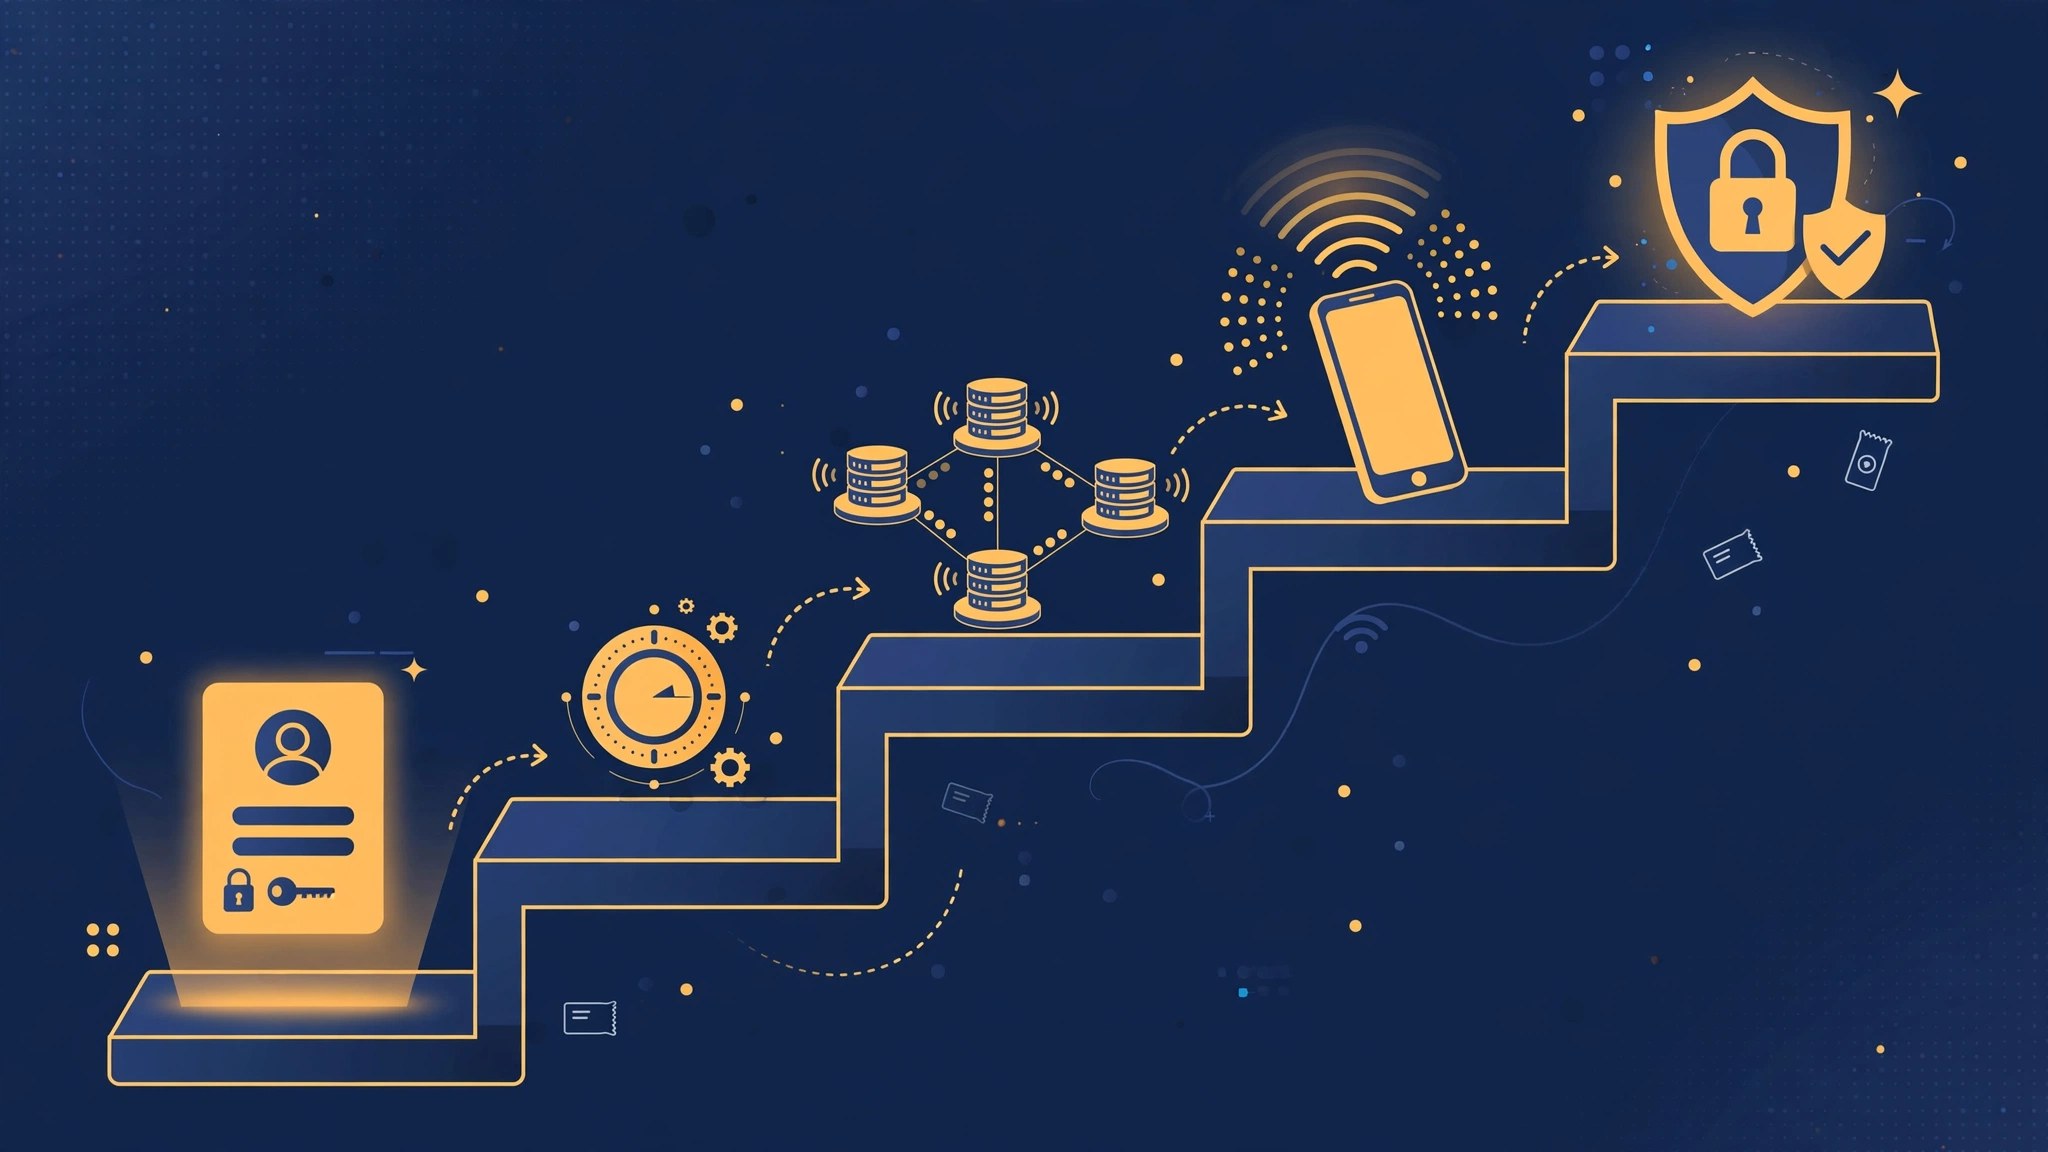
The fix ladder (in order)
Step 1: Disconnect the VPN and complete the captive portal login. Turn the VPN fully off — not just disconnected, but quit the app if it auto-reconnects. Open a browser and visit a deliberately unencrypted site such as http://neverssl.com, which exists specifically to trigger captive portals. Complete whatever login, code entry, or terms acceptance appears. Only then reconnect the VPN. A hotel-Wi-Fi fix guide by TechTippr puts this first for good reason: it is the single most common cause, and every later step is wasted if the portal is not done.
Step 2: Switch the protocol. In your VPN app’s settings, change the protocol. Try in this order: the app’s obfuscated or “stealth” mode if it has one (designed to look like ordinary web traffic); WireGuard; OpenVPN over TCP; IKEv2. The obfuscated/TCP-443 options exist precisely for hostile networks — this is what they are for.
Step 3: Try a different server. If the protocol switch did not help, the network may be blocking server IPs rather than protocols. Try two or three different servers in the same country. Large providers have big server pools; one blocked IP does not mean all are blocked.
Step 4: Check for a network-level VPN block notice. Some corporate and school networks state plainly that VPNs are not permitted. If the network’s acceptable-use page says so, no protocol trick is appropriate — you are on someone else’s network under their rules. Use mobile data instead (step 5).
Step 5: Bypass the Wi-Fi entirely with your phone’s hotspot. Connect your laptop to your phone’s mobile data hotspot and run the VPN over that. Mobile networks do not run the hotel-style filters that break VPNs, so this works essentially every time. It costs mobile data, which is why it is last — but it is the reliable fallback when the Wi-Fi is impenetrable or explicitly anti-VPN.
Special cases
The portal keeps reappearing every hour. Some hotel networks expire the login session and demand re-authentication. Each time, the VPN must be off for the re-login, then back on. There is no way around the ordering — the portal cannot work through the tunnel.
The portal page will not load even with the VPN off. Close all browser tabs first — an open HTTPS tab can confuse the portal detection — and try the unencrypted trigger site again. On phones, toggling Wi-Fi off and on forces the operating system to re-run its captive-network detection.
Everything works except one app or site. That is not a public-Wi-Fi problem; the destination is blocking the VPN’s IP address (streaming services do this routinely). Switch servers or accept it for now.
You need the VPN for work and nothing connects. Some corporate VPNs (as opposed to commercial privacy VPNs) use protocols that public Wi-Fi filters aggressively. Your IT department’s documented fallback — often a TCP-443 or SSL-based option — is the answer; commercial-VPN tricks do not apply to managed corporate clients.
When to give up on that network
Give up and use mobile data when: the network’s terms prohibit VPNs; you have tried the portal login, two protocols, and three servers; or the connection “succeeds” but no traffic flows (a sign of deep packet inspection silently killing the tunnel). Do not keep hammering connect — repeated failed handshakes against an actively filtering network will not suddenly succeed, and on metered hotel Wi-Fi you are burning money. Also: never “fix” a blocked VPN by turning the VPN off and doing sensitive work on the open network. An unprotected public network is worse than no network — wait for mobile data.
What this means for you
- Always complete the captive portal login with the VPN fully off, then connect the VPN. Order matters.
- The unencrypted trigger site (http://neverssl.com) is the fastest way to summon a missing portal page.
- Switch protocol before switching providers: obfuscated/stealth mode or OpenVPN TCP on port 443 beats most Wi-Fi filters.
- Once connected, run our 2-minute check to confirm the VPN is actually working — connecting is only half the battle.
- Wondering whether to bank over that hotel Wi-Fi? Read whether a VPN is safe for online banking first.
- Try 2–3 servers in the same country — the network may block IPs, not protocols.
- The phone-hotspot fallback works essentially every time; budget mobile data for it when you travel.
- If the network’s rules prohibit VPNs, respect that and use mobile data instead of fighting the filter.
Sources
- NSA and CISA — guidance on selecting and hardening VPN solutions
- Cybersecurity Dive — CISA mobile communications best practice guidance

Shoaib Hassan
Shoaib Hassan is the founder and editor of AuTechWire, an independent technology publication covering broadband, mobile networks, privacy, startups, and consumer tech.
Related Stories
Crypto Hacks Are Surging but Stealing Less — Here’s Why
In brief On October 22, 2026, Haseeb Qureshi, managing partner of the crypto investment firm Dragonfly, said cybersecurity…
ARTEX: The AI Pentesting Tool Used in the ConnectWise Hack
In brief On October 21, 2026, Microsoft said a China-state aligned group it tracks as Storm-0940 used an…
Chrome Wants to Catch Scams Before You Paste the Damage Into Your Terminal
In brief On October 20, 2026, Google announced three additions to Chrome's Enhanced Protection mode: a new two-tier…