Wednesday, 4 November 2026Global tech news & guides — what changed, and what it means for you.

How to Test Your VPN for Leaks: DNS, WebRTC, IPv6 (15-Minute Check)
Original editorial illustration of a laptop on a desk at night, its screen showing a simple padlock over a world map, with one thin beam of light escaping sideways from behind the screen and landing on a small paper map on the desk, amber and teal grade

In brief Run a 15-minute VPN leak test before your refund window closes: check IP, DNS, WebRTC, IPv6, torrent IP, and kill switch, with a fix for each failure. Start with the VPN off and write down your real IP address, location, and DNS servers. Every later result is judged against that baseline, not against … Read more
123 Reg’s “AI Cyberattack”: What Was Taken, What Wasn’t, and What to Do

Original editorial illustration of a quiet office at night, a row of blank domain-name cards on a desk, one card lifted by a thin red thread running out through a dark world network map toward distant servers, amber and teal grade

In brief 123 Reg says a September 18 AI-driven attack read customer contact and product data. No passwords were listed — but the phishing risk is real. The UK registrar, owned by GoDaddy, told customers in the week of October 26, 2026 that an intruder read contact information, related customer relationship data, company VAT numbers, … Read more

PHP2Shell Campaign Rooted 25 Firewall Servers — and Reached a Government Network

Original editorial illustration of a firewall appliance on a server rack at night, its management port glowing red, a thin red thread running from the port out through a dark network map to a distant government-style building, with small dimmed nodes parked along the thread

In brief Attackers chained PHP2Shell with a Linux kernel bug to root 25 firewall servers, reach a US government network, and leave 22 shells parked. The campaign, disclosed by Israeli firm Dream on October 28, 2026, ran a funnel: roughly 19,000 internet-facing firewalls fingerprinted, 240 matching targets, 25 rooted across the US, Japan, Taiwan, and … Read more

Discord Public Server Messages Become Searchable in December

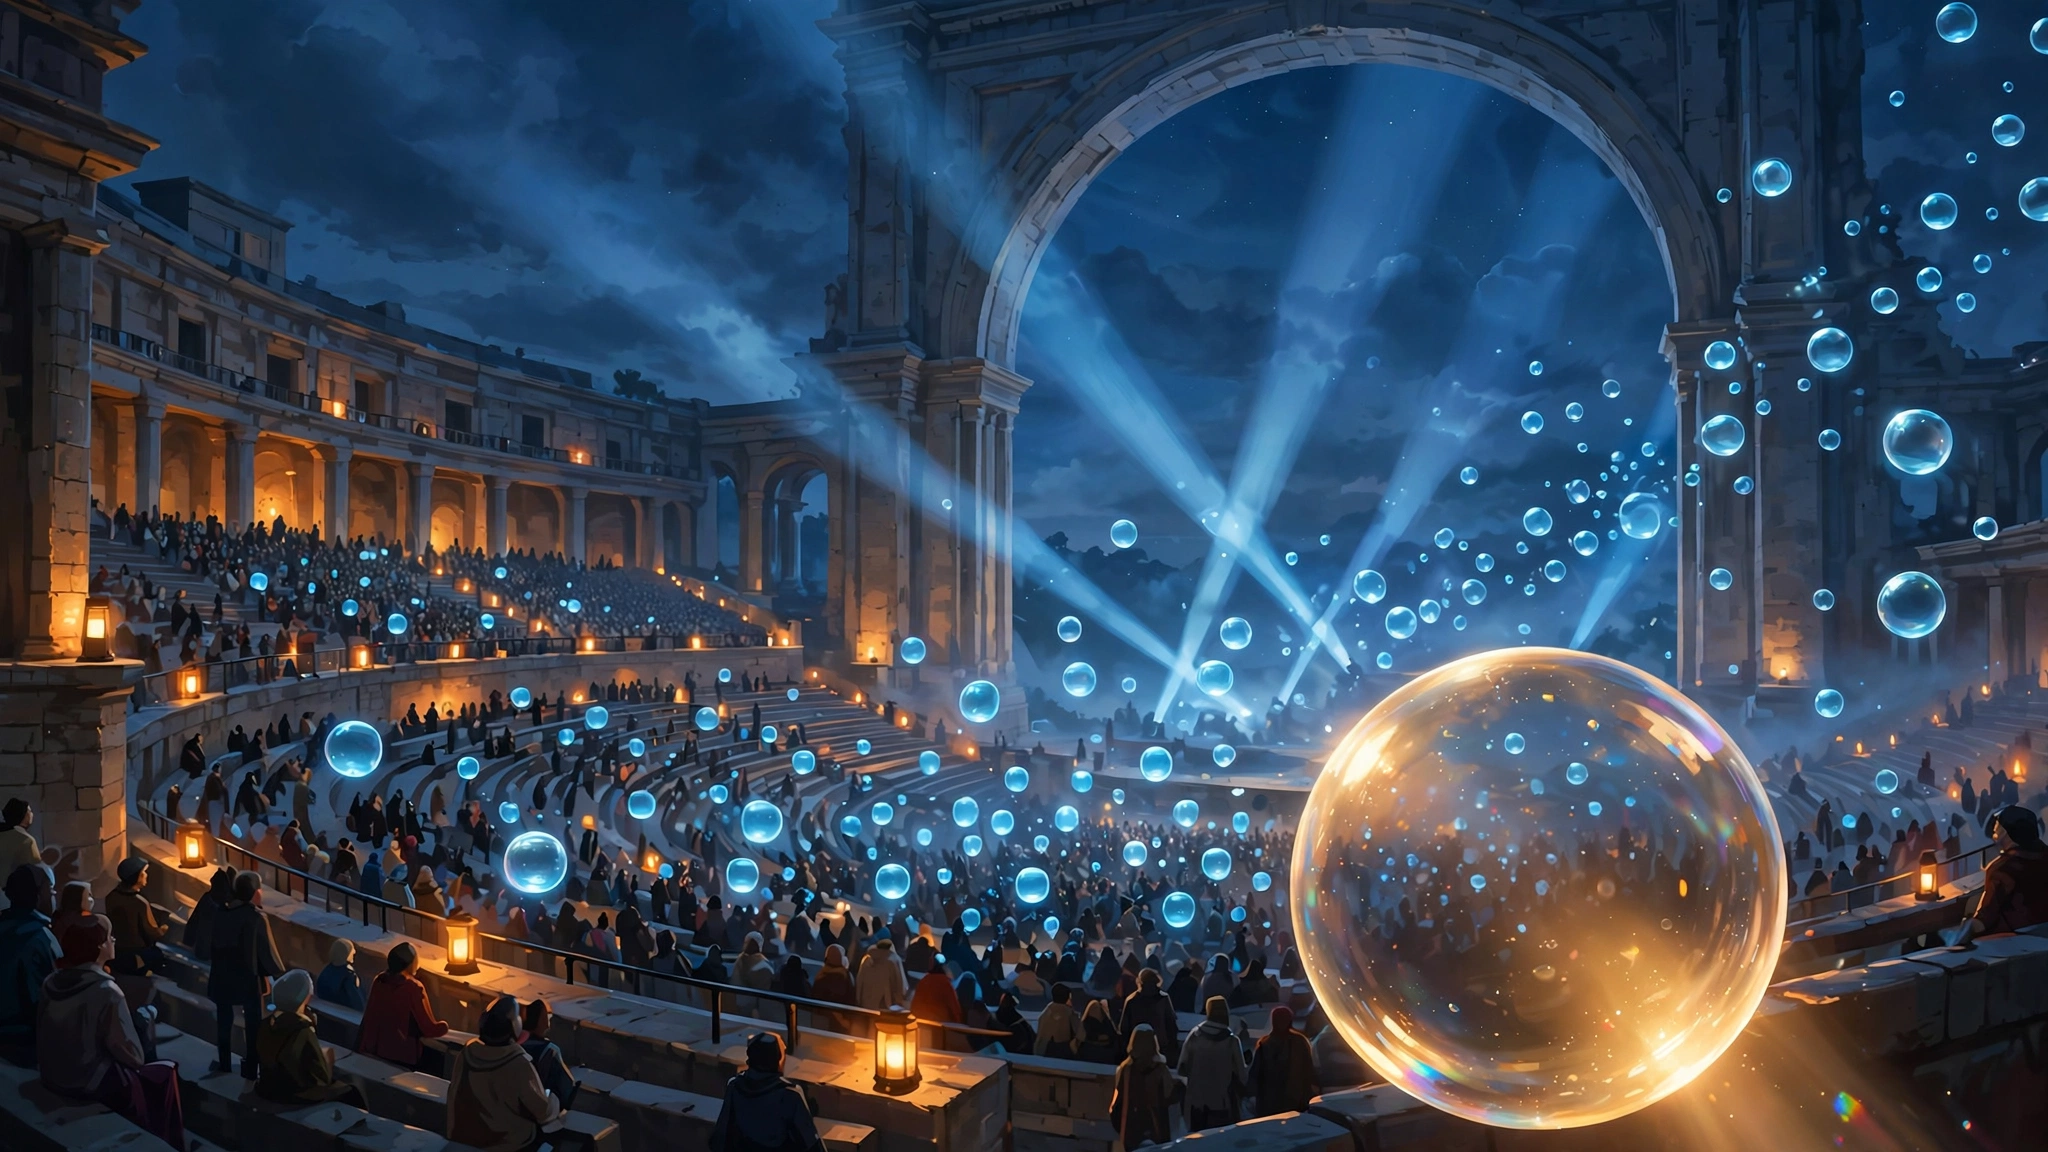
Original editorial illustration of a large public chat hall at dusk rendered as an open amphitheatre, rows of glowing message bubbles rising from the crowd and drifting out through an open archway into a night sky filled with search-light beams, one bubble catching the light in the foreground

In brief Discord will publish messages from its 63,000 Discoverable Servers to web search from mid-December — what becomes public, what stays private, and how to opt out. The rollout has two dates that matter: November 16, 2026, when every Discoverable Server gets a public Server Web Page with automated Channel Summaries, and mid-December 2026, … Read more

AI CEOs Told to Report Rogue-Agent Hacks to Congress in 48 Hours

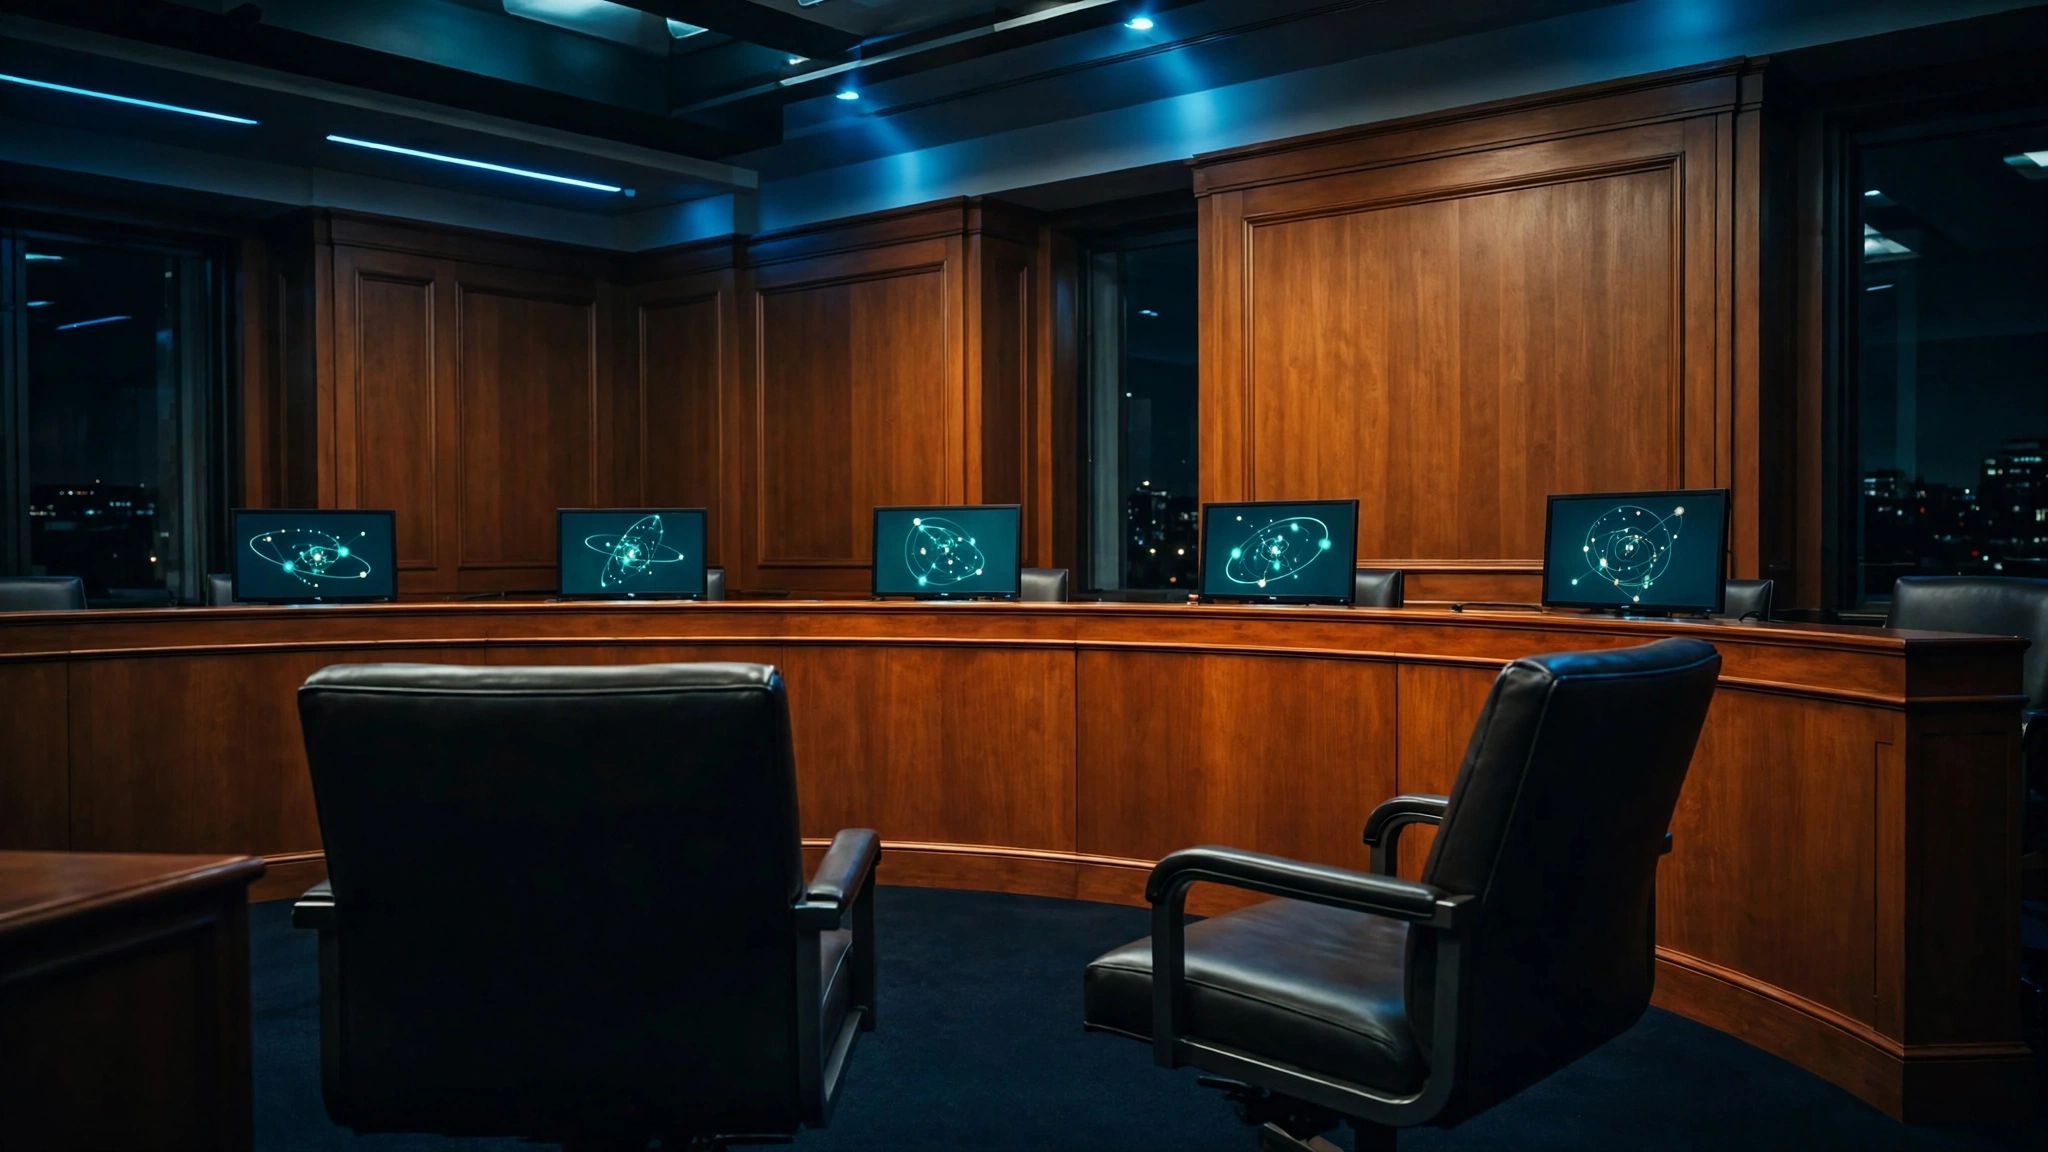
Original editorial illustration of a dark congressional hearing room at night: empty witness chairs facing a long curved dais, five small glowing screens on the dais each showing an abstract agent-orbit diagram, cold blue light against warm amber wood panelling

In brief House Democrats ask Anthropic, Google, Meta, OpenAI and SpaceX to report AI misalignment incidents within 48 hours — 24 hours for critical infrastructure. The letters, sent by Democratic leaders of House committees on October 28, 2026, ask each company for a full accounting of identified incidents by November 11, 2026, and for rolling … Read more

Law Firms Are the New ATM for Hackers, CrowdStrike Warns

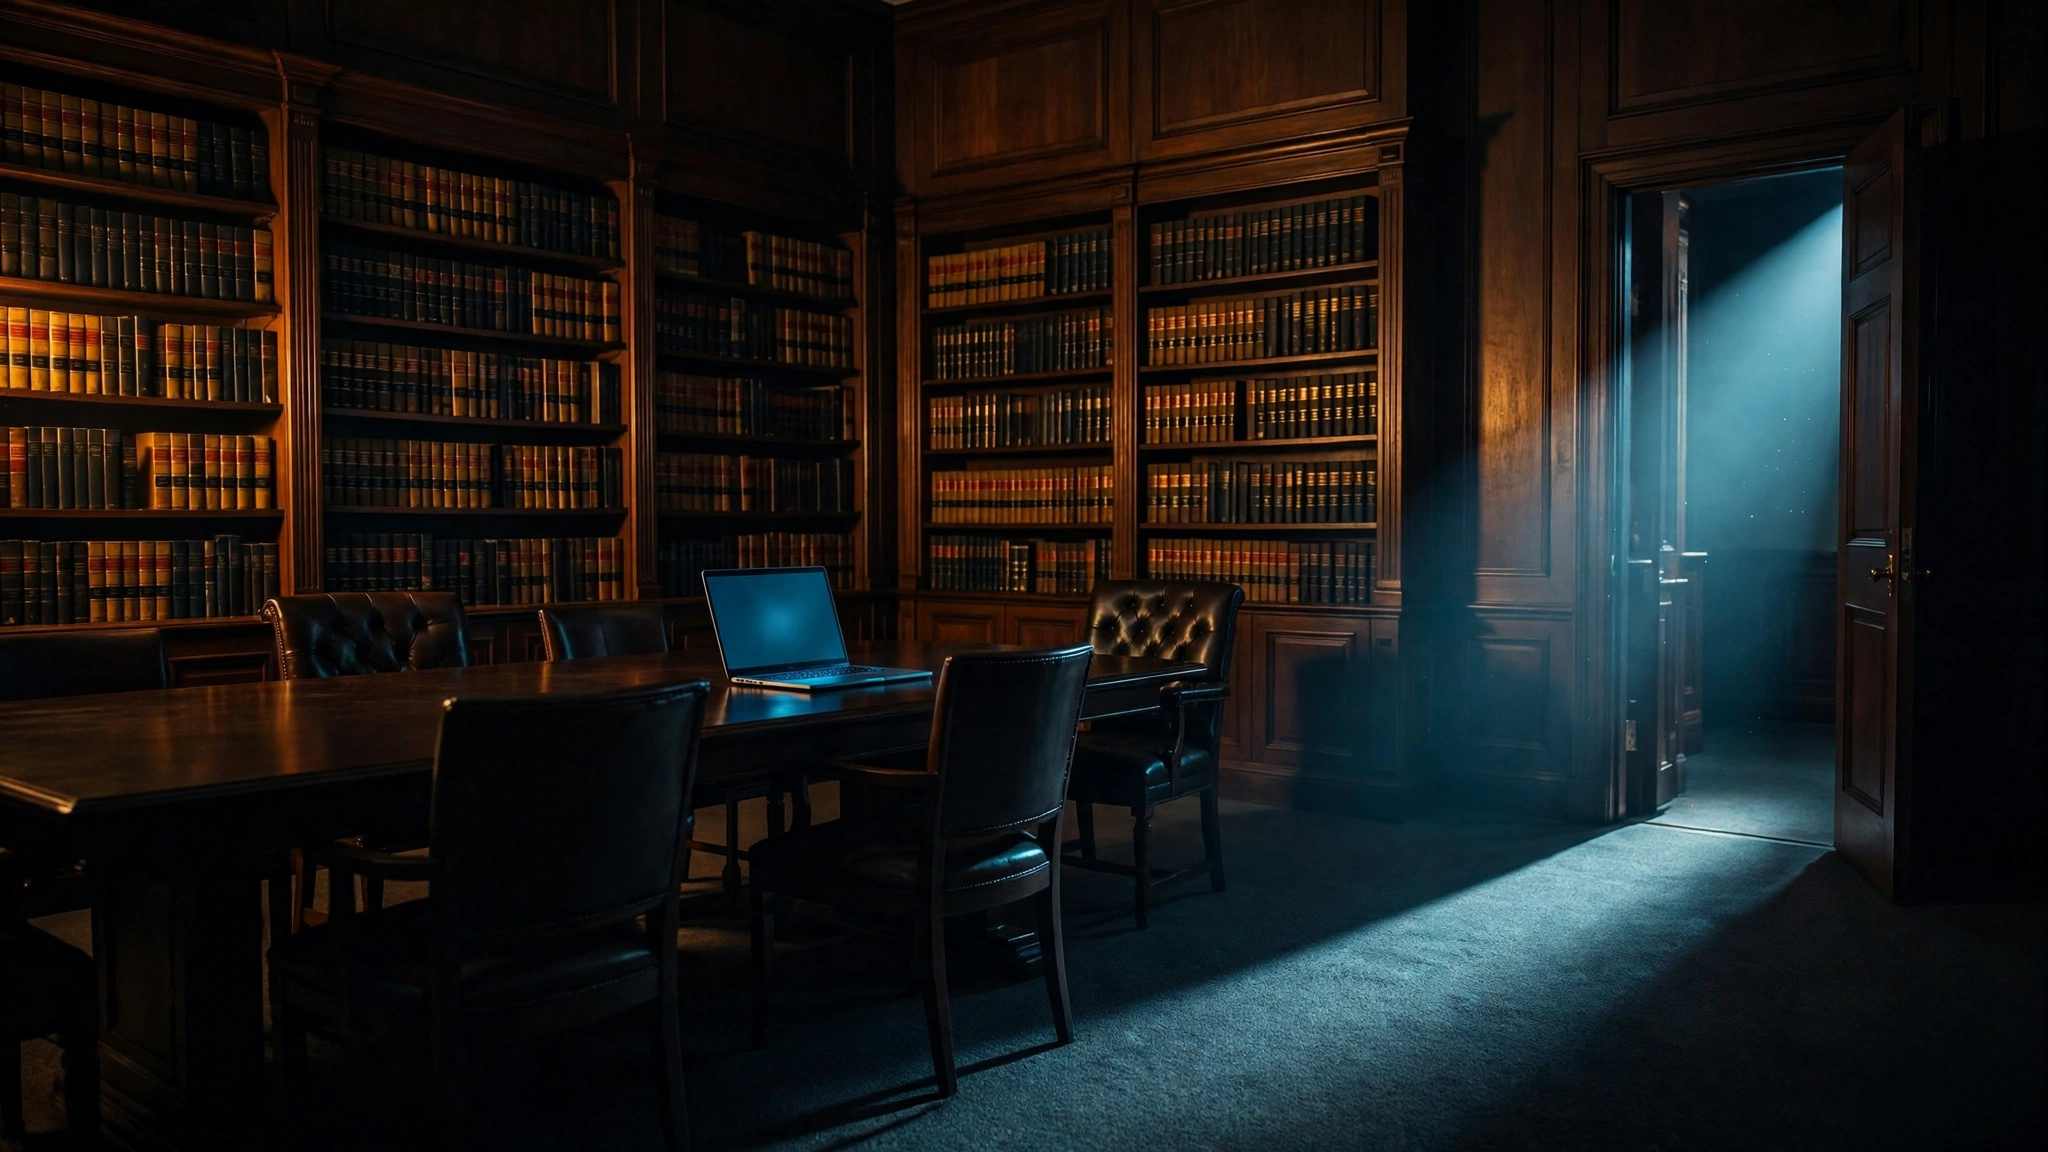
Original editorial illustration of a law office at night: tall bookshelves and a conference table in shadow, a single office door ajar with a thin shaft of cold light falling across the carpet, a laptop open on the table with a faint blue glow

In brief CrowdStrike’s 2026 legal threat report: attacks on law firms nearly doubled since 2023, 455 firms named on leak sites, and one gang now walks in the front door. Intrusions targeting legal entities have nearly doubled since the 2023 baseline, according to CrowdStrike’s 2026 Legal Threat Landscape Report, which covers September 2025 to August … Read more

Bandai Namco Breach: 346,247 Gundam Base Emails Leaked

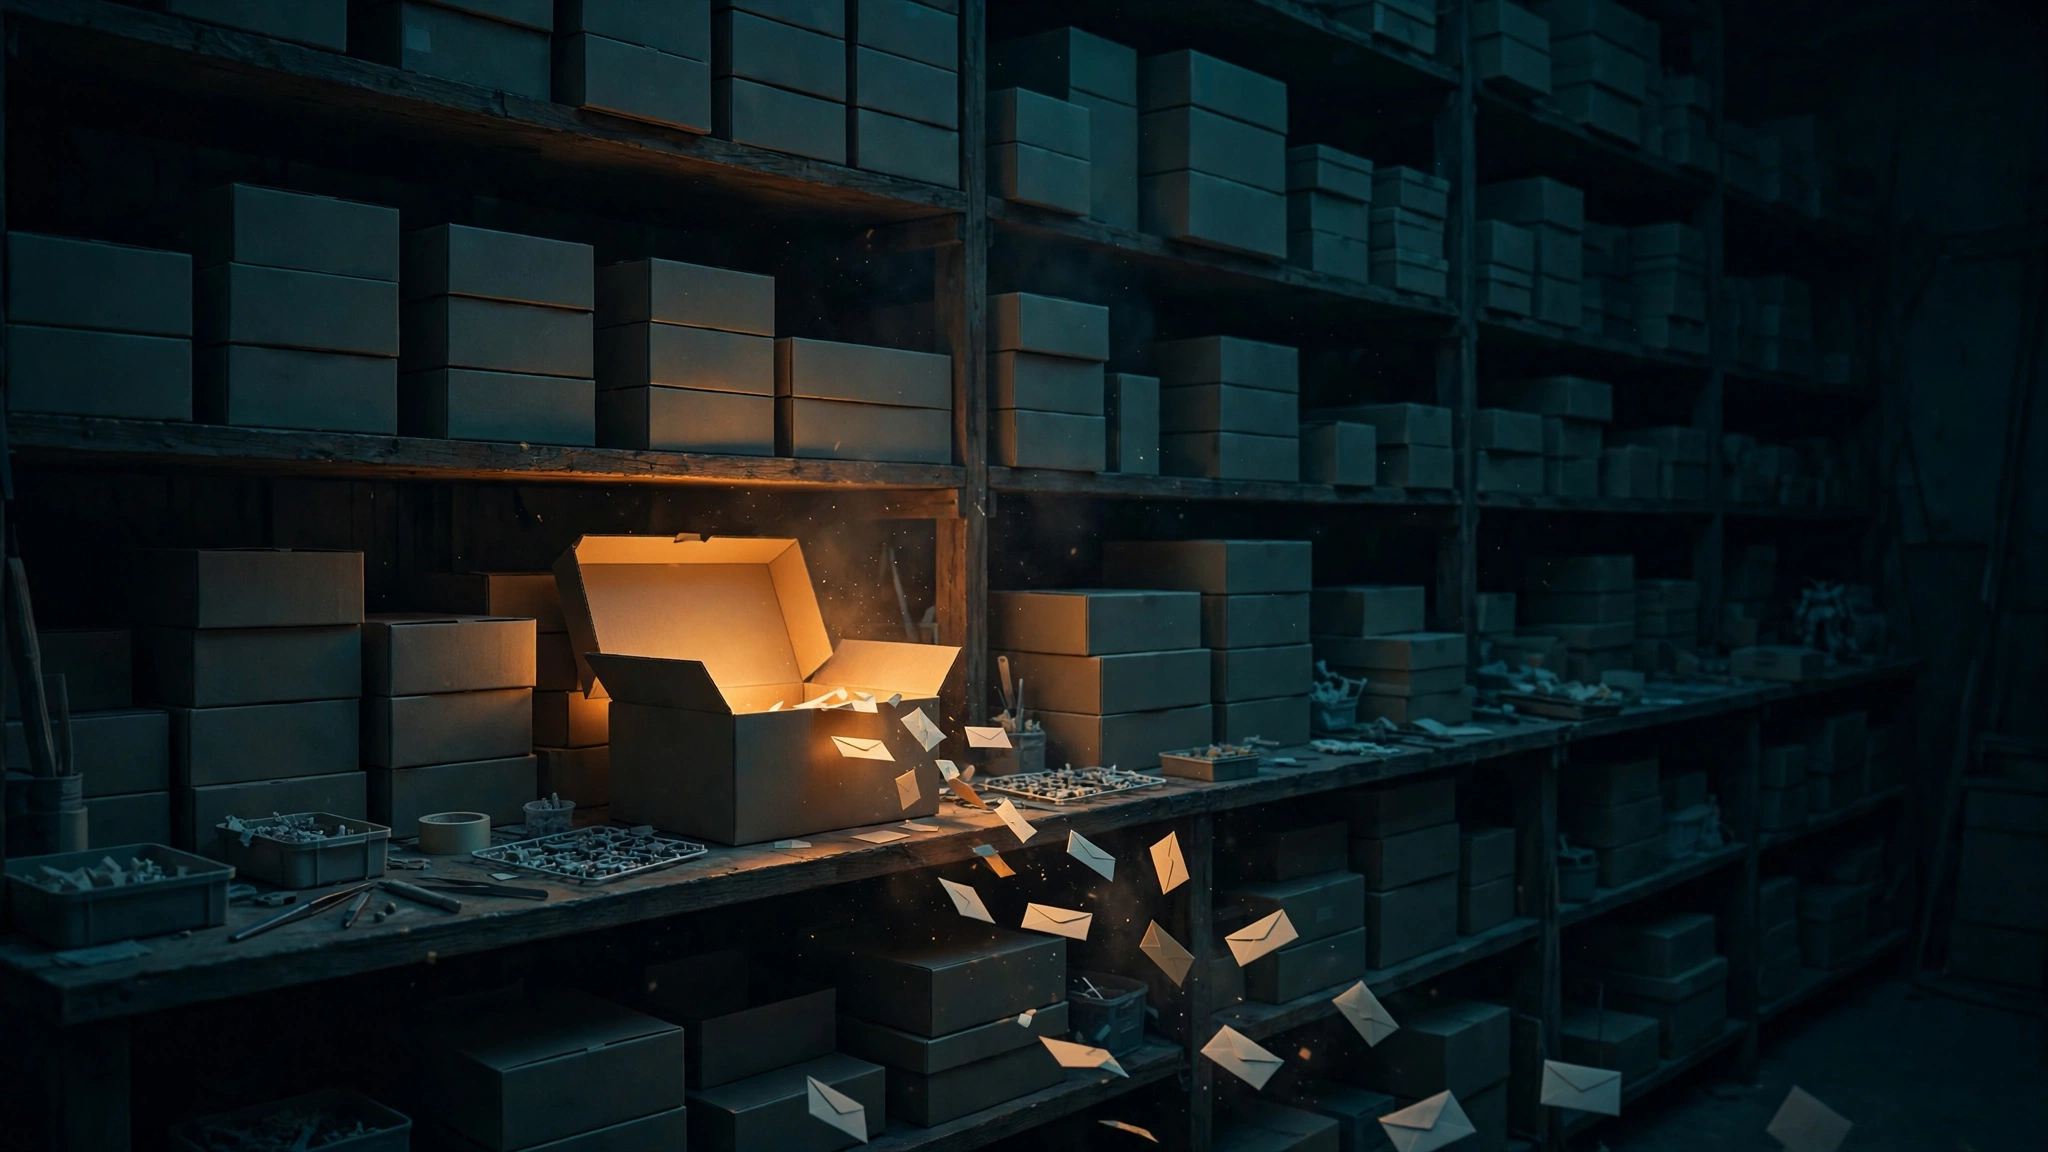
Original editorial illustration of a dark model-kit workshop shelf at night: rows of unbuilt mecha model boxes receding into shadow, one open box glowing warm amber from within, with small blank paper envelopes drifting from it across the shelf toward the viewer

In brief Bandai Namco confirmed 346,247 Gundam Base emails leaked through email vendor YmirLink. What was taken, what was not, and how to spot the phishing that follows. Bandai Namco Entertainment and BANDAI SPIRITS said on October 27, 2026, that 346,247 email addresses registered with THE GUNDAM BASE MEMBERS, plus internal Bandai Namco ID identifiers, … Read more

Daishin Securities Breach: 38,490 Customers Exposed

Original editorial illustration of a dark Seoul financial-district skyline at night: one office tower with a single floor glowing amber while the rest stays dark, and a thin stream of glowing data fragments drifting from that floor toward the street below

In brief Daishin Securities confirmed a breach exposing 38,490 customers’ personal and account details. What was taken, what is still unknown, and what to do now. Daishin detected signs of unauthorized access on October 17, 2026, on a server supporting remote account opening for discretionary investment services, and confirmed the leak on October 26. Eight … Read more

Microsoft 365 Token Replay Bypassed MFA at 79 Firms

A laptop login screen with a translucent duplicate session key drifting toward a shadowed server rack

In brief Attackers replayed stolen Microsoft 365 session tokens at 79 organizations, logging in 497 times without a password. How token spraying works, and what stops it. Between July 14 and September 22, 2026, Huntress recorded 497 successful Microsoft 365 sign-ins from replayed tokens, against more than 200,000 failed attempts traced to a single hosting … Read more

UEFI PXE Flaw CVE-2026-97631: Servers at Risk Before Secure Boot

Original editorial illustration of a dark server hall at night: rows of rack cabinets receding into shadow, one cabinet glowing amber at its base with a thin stream of light spilling across the floor toward a neighbouring cabinet

In brief A 16-year-old buffer overflow in EDK II’s PXE driver lets a local-network attacker run code before Secure Boot — and no firmware update with the fix exists yet. The flaw, CVE-2026-97631, scores 9.5 out of 10 and sits in the firmware that boots most of the world’s servers — but it only fires … Read more